
Supabase Exposure Shows Vibe-Coding Security Risk
Thousands of Supabase-hosted databases were found publicly exposing personal data, highlighting security gaps around AI-built apps.
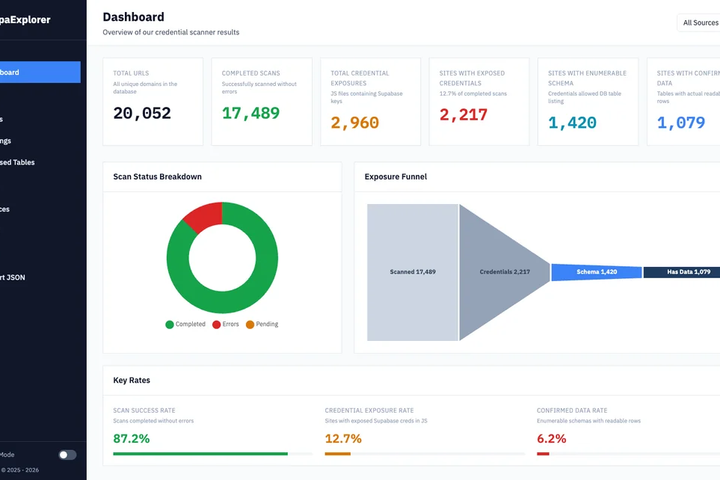
The rise of vibe-coded applications is creating a familiar security problem at much larger speed.
What happened
A cybersecurity firm found around 16,000 Supabase-hosted databases where some degree of personal data was publicly exposed.
The exposed information included names, addresses, phone numbers and in some cases passwords or authentication tokens. The issue was linked to customer configuration rather than a single central breach.
Supabase has become a popular backend for developers and non-traditional builders creating apps quickly, including with AI coding tools.
Why it matters
AI coding tools make it easier for more people to ship applications, but they do not automatically teach secure backend configuration.
If builders deploy apps without understanding database permissions, authentication and access policies, sensitive data can become public even when the underlying platform works as designed.
That makes this a broader AI-adjacent security risk, not only a Supabase issue.
The bigger picture
The software market is entering an era where app creation is becoming easier than secure app operation.
As AI lowers the barrier to building, platforms will need stronger defaults, clearer warnings and automated security checks to prevent misconfigured apps from becoming data-exposure incidents.