Rafay and Fortanix bring confidential AI to Kubernetes workloads
The joint offering combines confidential containers, cryptographic attestation and deployment controls for AI workloads.
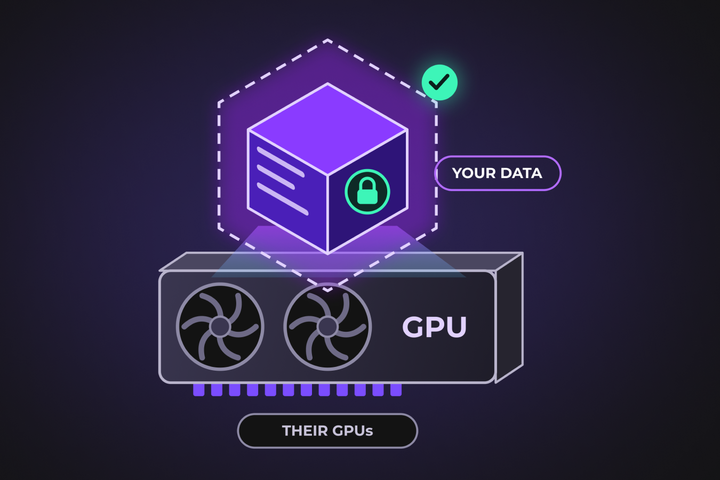
Running AI on someone else’s infrastructure raises a practical question: when should that infrastructure receive the keys to sensitive data?
What happened
Rafay and Fortanix launched an available joint offering using Confidential Containers and hardware-based trusted execution environments. Fortanix checks the environment and workload through cryptographic attestation before releasing keys. Rafay supplies deployment, tenant management and access controls.
Why it matters
Sensitive inputs and proprietary model weights can require protection while they are being used, not just while they are stored or transferred. Combining these controls with orchestration gives cloud operators a more integrated service to offer.
The bigger picture
Confidential computing brings hardware security and software operations into the same deployment process. The joint offering connects an existing security capability to the tools used to run Kubernetes workloads.