
ClickFix Attacks Hijack Trusted Brand Ads
Attackers use compromised brand advertising accounts to spread ClickFix malware through trusted platforms.
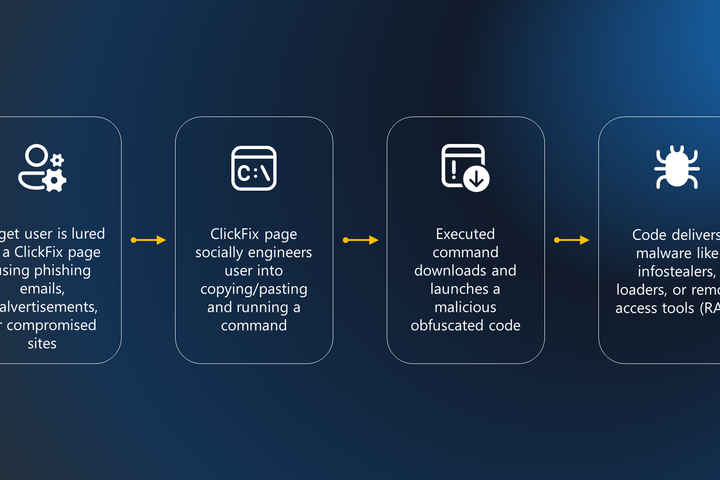
The ClickFix malware technique is spreading through compromised advertising accounts, including a campaign that abused an HBO Max Reddit account to distribute malicious ads.
What happened
Victims were directed to fake websites or CAPTCHA-style prompts that instructed them to copy commands into their own terminals. Running those commands installed information-stealing malware. Reddit confirmed that the advertising account had been compromised and removed the malicious content.
Why it matters
ClickFix is effective because it avoids many conventional exploit techniques. Instead of breaking software directly, attackers convince users to execute the malicious command themselves.
Using verified brand accounts and legitimate ad infrastructure makes those instructions appear more trustworthy and can bypass users' normal suspicion of unknown websites.
The bigger picture
Cyberattacks are increasingly exploiting trusted distribution channels rather than only technical vulnerabilities. Advertising networks, support accounts and collaboration platforms can all become delivery mechanisms. Security teams therefore need to monitor identity and account compromise as closely as malware signatures or software exploits.